What is Splunk, How it Works, and What it Does for IT Leaders
Splunk is a machine-data platform with separately licensed SIEM, SOAR, ITSI, and observability products. Learn how its indexing, workload pricing, and Cisco changes work.
What Is Splunk?
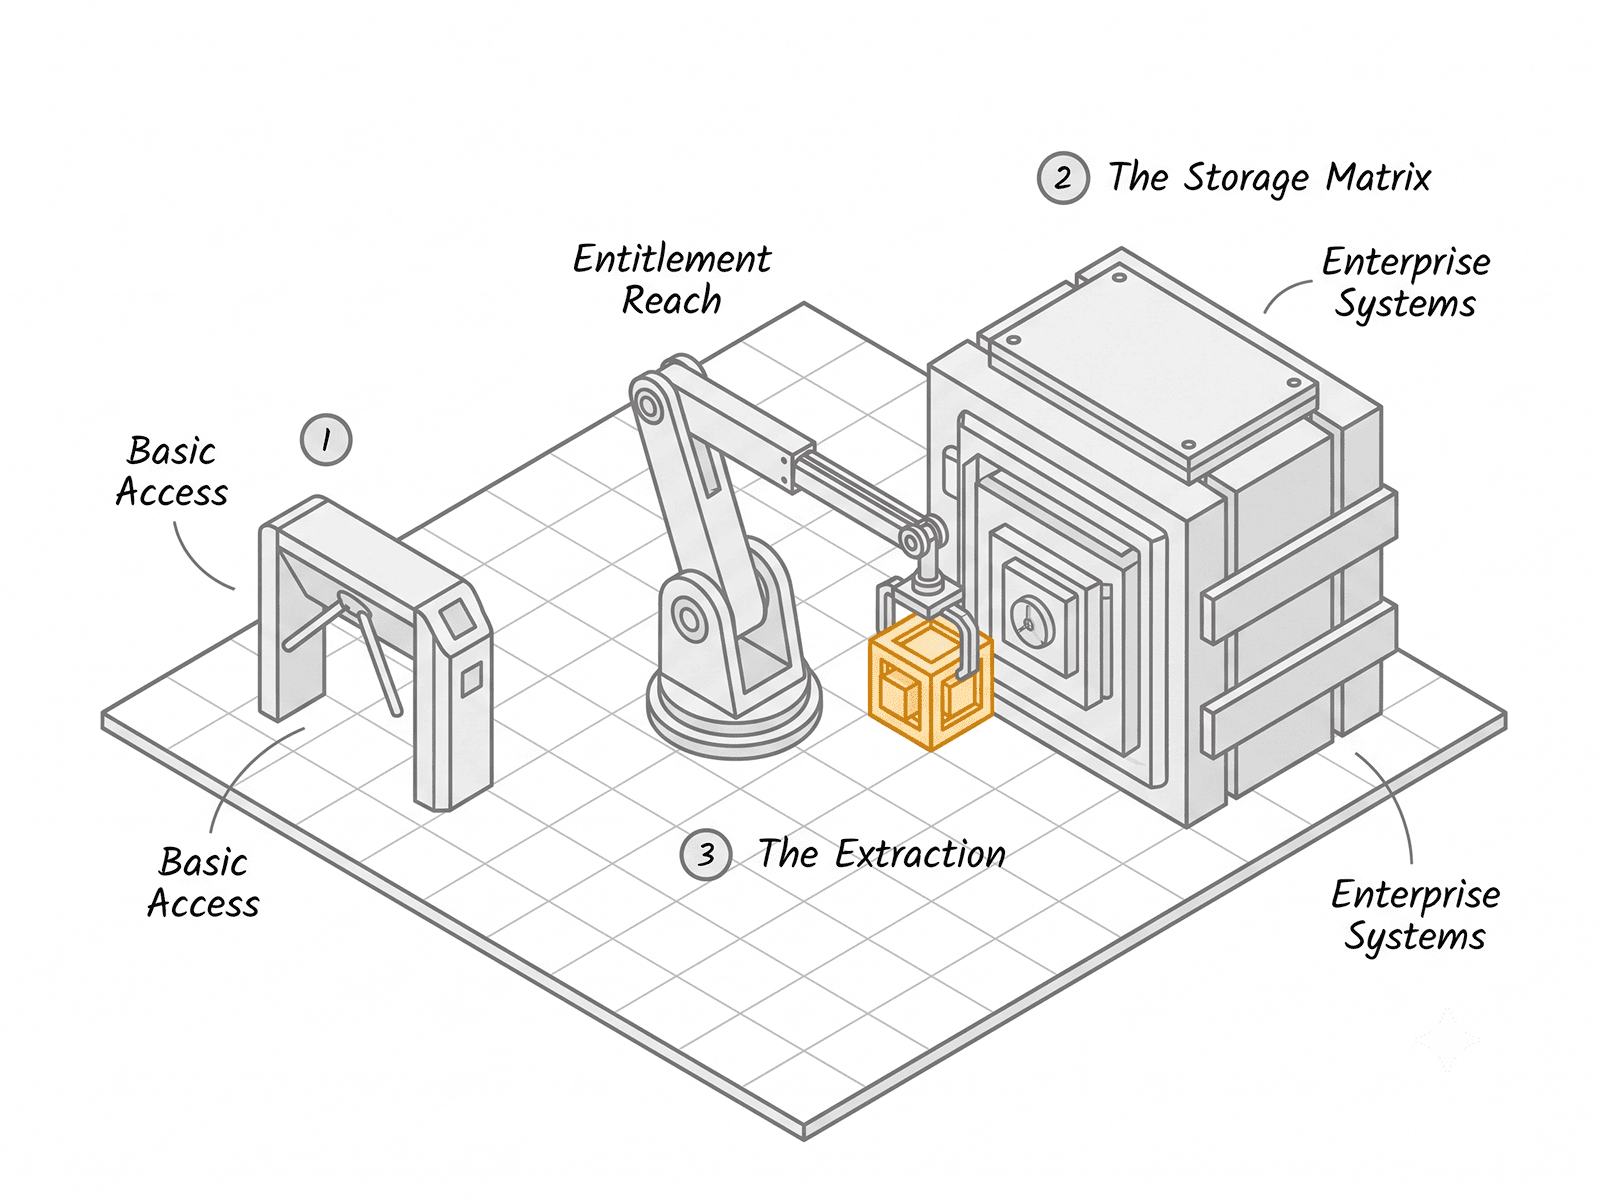
Splunk is a machine-data platform. It collects logs, metrics, and events from almost any system, indexes them, and lets you search, alert on, and visualize that data with its own query language, SPL. Security, IT operations, and observability products run on top of the platform, and each one carries its own license.
The common shorthand calls Splunk a SIEM. Splunk's SIEM is one product on that platform, Splunk Enterprise Security, sold in two editions. The same data layer also runs service health monitoring, application performance tools, and plain search across anything you send it.
Ownership changed in 2024. Cisco completed the acquisition on March 18, 2024, and Splunk now operates as a wholly owned Cisco subsidiary.
In practice:
- Splunk Enterprise is the self-managed platform you run on your own infrastructure.
- Splunk Cloud Platform is the same platform as Splunk-managed SaaS on AWS, Google Cloud, or Microsoft Azure.
- Premium applications such as Enterprise Security, SOAR, and IT Service Intelligence (ITSI) sit on the platform and are licensed separately.
- Splunk Observability Cloud and Splunk AppDynamics handle application and infrastructure monitoring under host-based pricing.
Splunk earns its cost in large, mixed environments: hundreds of log sources, a security team that writes its own detections, and retention obligations an auditor will test. I have watched smaller teams buy it for the name and then struggle to staff it.
It's budget season; let's see how you do
Budget comes up in about 88% of the thousands of conversations we have with IT leaders. So we made a game about it. Play to find out what your year-end board meeting looks like.
Play game
How Does Splunk Work?
Every deployment, cloud or self-managed, moves data through the same stages. Knowing where each stage happens tells you where performance problems start and where the bill grows.
1. Data Collection: Forwarders, HTTP Event Collector, and Add-ons
The universal forwarder is a lightweight agent that ships data from hosts with minimal processing. A heavy forwarder can parse, filter, and route data before it reaches the indexers. The HTTP Event Collector (HEC) accepts events over HTTP, which suits SaaS tools and applications that push data instead of writing files.
Add-ons from Splunkbase supply source-specific inputs and field definitions. Cloud security services are a typical case: a Zscaler deployment generates web and private access logs that usually arrive through a vendor add-on or a streaming feed.
2. Pre-Index Processing: Ingest Actions, Edge Processor, and Ingest Processor
This stage decides how much data you pay to index. Ingest actions apply filtering and routing rules inside the platform. Edge Processor runs on your infrastructure at the network edge, while Ingest Processor is Splunk-hosted, and both use SPL2 pipelines to filter, mask, and route data, including to Amazon S3.
According to Splunk Lantern, Edge Processor comes with Splunk Cloud Platform and Splunk Enterprise subscriptions at no added cost. The Essentials tier of Ingest Processor is included with Cloud Platform. If neither is deployed in your environment, you are almost certainly indexing data nobody searches.
3. Parsing, Indexing, and Storage Buckets
At index time, Splunk breaks the incoming stream into events, extracts timestamps, and assigns default fields such as host, source, and sourcetype. Events land in indexes and age through hot, warm, cold, and frozen buckets. Frozen data is deleted or archived, and archived buckets can be thawed for search.
Retention is set per index, so a firewall index and a DNS index can follow different rules. Splunk Cloud Platform abstracts the buckets into searchable storage and an optional archive, covered in the compliance section below.
4. Schema-on-Read: Why Splunk Extracts Fields at Search Time
This is the design choice that explains Splunk. Apart from the defaults, Splunk extracts fields when a search runs. Splunk's indexing documentation recommends doing "most knowledge-building activities" at search time and warns that custom index-time extraction can slow both indexing and searching.
The benefit is fast onboarding. You can ingest a new source on day one, define its fields next week, and change those definitions later without re-ingesting anything. That flexibility is why Splunk became the tool teams reach for when they need to search everything.
The trade-off is that every search pays the parsing cost. In my experience this is also the root of Splunk's cost reputation, because deferring structure makes it easy to index everything raw. Under ingest pricing that raw volume was the bill, and under workload pricing the search-time work consumes the compute you pay for.
Splunk's acceleration features, such as data model acceleration, exist because pure search-time work gets expensive at scale. The table below shows which work happens when.
5. Search: SPL, Search Heads, and Indexers
You query Splunk with the Search Processing Language (SPL), a pipe-based language in which each command transforms the output of the one before it. Search heads coordinate queries, and indexers run the search work on the data they hold. Indexer clustering replicates data for availability, and search head clustering scales the query tier.
6. Knowledge Objects and the Common Information Model (CIM)
Field extractions, lookups, tags, event types, and data models are saved as knowledge objects that any search can reuse. The Common Information Model normalizes field names across vendors, so a failed-login detection behaves the same for Okta, Entra ID, and a Linux host. Enterprise Security correlation searches are written against CIM data models, so a source without CIM mapping stays invisible to that content.
Mapping is real staff work. Splunk's own August 2026 platform update acknowledges that CIM onboarding can take weeks. Splunk has announced AI-assisted tools that recommend mappings and flag sources that drift out of compliance.
7. Action: Alerts, Correlation Searches, and Automated Response
Scheduled searches drive alerts, reports, and dashboards. In Enterprise Security, correlation searches feed risk-based alerting, and Splunk SOAR runs playbooks that act on what the detections find.
8. Federated Search: Querying Data Outside the Index
Federated search lets Splunk query data where it lives. Splunk's federated search documentation (version 10.5.2605, July 2026) lists seven options. Only Federated Search for Splunk, which queries other Splunk deployments, works on Splunk Enterprise; the rest are Splunk Cloud Platform features.
The Amazon S3 and Azure Databricks options require Cloud Platform deployments in AWS regions, and federated scans draw on a separate Data Scan Units license. Splunk positions the feature for "low-frequency, ad-hoc searches," so I treat it as a home for cold, rarely queried data. Detections and dashboards still belong on indexed data.
Splunk Product Architecture: Platform, Enterprise Security, SOAR, ITSI, and Observability
Splunk is a family of products sharing one data layer, each solving a different problem and each licensed on its own terms. Evaluations go sideways when one person says Splunk and means the platform, while another means Enterprise Security.
Splunk Platform (Splunk Enterprise and Splunk Cloud Platform)
What it does: Collects, indexes, and searches machine data, with dashboards, alerting, and SPL. Splunk Enterprise runs on your infrastructure, while Splunk Cloud Platform is Splunk-managed SaaS on AWS, Google Cloud, or Azure.
Problems it replaces:
- Separate log tools that each see one slice of the environment
- Self-built log stacks that need constant maintenance
- Manual evidence gathering during incidents and audits
When you need it: When you have dozens of log sources, several teams need to search them, and policy dictates how long you keep the data.
Key capabilities: distributed search and clustering, per-index retention, pre-index processing, federated search (mostly on Cloud Platform), and the Splunkbase app ecosystem.
Splunk Enterprise Security (Essentials and Premier)
What it does: Enterprise Security (ES) is Splunk's SIEM. It turns indexed security data into detections, risk scores, investigations, and cases.
Problems it replaces: legacy SIEMs that can't keep up with data volume, and alert triage spread across separate consoles.
When you need it: When a SOC exists or is forming and needs correlation across many sources, with case management.
Key capabilities: the table below breaks them down by edition, drawn from Splunk's ES editions overview.
UEBA is the edition decider. Splunk's UEBA page states that UEBA is unavailable as a standalone product or as an add-on to Essentials, so if behavioral analytics is a requirement, you are buying Premier. Our SIEM vendor guide compares ES with Sentinel, QRadar, Exabeam, Securonix, and Sumo Logic.
Splunk SOAR
What it does: Runs automated playbooks that enrich alerts, query other tools, and take response actions such as blocking an IP address or disabling an account. It was called Splunk Phantom before the rename.
Problems it replaces: manual runbooks and copy-paste triage between consoles.
When you need it: When alert volume outgrows the team and analysts repeat the same enrichment steps on every alert.
Key capabilities:
- Prebuilt playbooks (Splunk claims more than 100)
- App connectors for third-party tools (Splunk claims more than 350)
- Cloud or on-premises deployment
SOAR ships natively in ES Premier, and a free Community license allows 100 licensed actions per day.
Splunk IT Service Intelligence (ITSI)
What it does: Models business services from their components, scores service health with KPIs, and groups related alerts into episodes.
Problems it replaces: infrastructure consoles that show green hosts while customers can't check out.
When you need it: When infrastructure and application data already lives in Splunk and leadership wants service-level health reporting.
Key capabilities: service models, KPI-based health scores, and event analytics with episode management. ITSI is licensed by ingest (up to 200 GB per day) or by workload.
Splunk Observability Cloud and Splunk AppDynamics
What it does: Observability Cloud covers APM, infrastructure monitoring, real user and synthetic monitoring, logs, and on-call, and Splunk describes it as OpenTelemetry-native. AppDynamics adds APM with on-premises and virtual appliance options. Cisco moved AppDynamics into the Splunk business unit in 2024 and later renamed it Splunk AppDynamics.
Problems it replaces: separate APM, infrastructure, and front-end monitoring tools.
When you need it: When distributed applications slow down and nobody can say where. Observability Cloud is SaaS only, so regulated estates that need on-premises APM look at AppDynamics.
Key capabilities:
- Host-based pricing from $15 per host per month
- A Free Edition for 15 hosts
- Log Observer Connect for logs already in the Splunk Platform, at no added cost
Which Splunk Product Fits Which Scenario
This is the adoption sequence I have seen work:
- Onboard and CIM-map your top sources on the platform.
- Add pre-index filtering before volume grows.
- Add ES Essentials when a SOC forms.
- Move to SOAR or ES Premier when alert volume outgrows the team.
ITSI and Observability follow separate tracks, usually owned by IT operations and platform engineering.
How Splunk Pricing Works: Workload, Ingest, Activity-Based, and Entity Models
Splunk publishes no list price for Splunk Cloud Platform, Splunk Enterprise, or Enterprise Security, so every deal starts with a quote. The only list price on Splunk's pricing page is Observability Cloud, starting at $15 per host per month.
What Splunk does publish is the metering, and that is where your negotiation should start. The Splunk Cloud Platform service terms state that subscriptions are workload-based, with ingest-based subscriptions offered "by exception." The same terms say a workload subscription places no meter on ingestion.
What a Splunk Virtual Compute (SVC) Unit Measures
An SVC is Splunk's unit of compute, memory, and I/O on Cloud Platform. Splunk Lantern says utilization is sampled every few seconds and reported hourly in the Cloud Monitoring Console. On Splunk Enterprise the workload unit is the vCPU of your own infrastructure, and Splunk's pricing FAQ says the per-vCPU price falls as you scale.
Under workload pricing, the bill grows with search concurrency, scheduled searches, correlation searches, data model acceleration, and premium app load. Storage is bought separately in blocks sized to your retention. The cost conversation moves from how much you send to how hard you search it.
What Grows the Bill Under Ingest Pricing
Ingest pricing meters uncompressed data indexed per day. On Cloud Platform, an ingest subscription includes searchable storage equal to 90 days of indexed volume, so 100 GB per day comes with 9,000 GB.
Splunk's service details let you exceed the daily volume up to five times in a calendar month. After that, sales engages about reducing usage or buying more, and Cloud Platform does not support license pooling.
Two more details surprise buyers. Cloud Platform places no limit on user counts. Premium apps such as ES and ITSI are licensed separately from the platform, on ingest or workload terms.
Activity-Based and Entity Pricing
Activity-based pricing, announced at .conf26 for Cloud Platform, uses two meters: ingest and search activity. Entity pricing counts hosts and containers for Observability Cloud and AppDynamics. Per Splunk's Observability pricing FAQ, billing uses the monthly average of hourly host counts, and Splunk does not auto-invoice overages.
The Cisco Data Rate and Cloud Flex
Splunk applies a 0.5x weighted rate to eligible Cisco data under a program it calls Integrated Enterprise Value. The documentation limits it to ingest-based licenses (Splunk Enterprise above 100 GB per day, or a Cloud Platform ingest license) and to listed Cisco sourcetypes. It lowers how much of your entitlement that data consumes, while the compute the data uses stays the same.
Splunk's pricing page also describes Cloud Flex, which lets you reallocate committed spend across the Splunk portfolio. Splunk does not publish Cloud Flex contract terms, so get them in writing before you rely on them.
What Changed After Cisco Acquired Splunk
The first visible change was organizational. Cisco moved its own observability business, including AppDynamics, into Splunk, and Splunk products have started appearing inside Cisco's own consoles.
The larger change is the Cisco Data Fabric. Splunk describes it as an architecture delivered through the Splunk Platform, with no separate product to buy. It has five components:
- Machine Data Lake, a Splunk-managed, low-cost tier
- Catalog, a data catalog
- Federated Search
- AI-assisted data management
- Agent Launchpad, a no-code agent builder called Agent Builder until June 2026
Separate what ships from what is promised. Splunk states that Machine Data Lake, Catalog, Agent Launchpad, and expanded Federated Search became generally available on August 4, 2026. Per Splunk's Cisco Live update, Splunk Platform, ITSI, and Observability Cloud inside Cisco Cloud Control remain in controlled availability.
On security, Cisco positions Cisco XDR and Splunk ES as complementary. Cisco's security blog describes XDR detections flowing into ES as findings without shipping the high-volume telemetry behind them. If XDR is on your shortlist, our MDR and XDR provider guide covers the managed options.
The practical question for buyers is whether federated search plus Machine Data Lake lets you keep low-value data out of the premium index. In my view it is the most useful thing Cisco has added, and the one most worth testing against your own query patterns before you renew.
What Splunk Offers IT Leaders
Splunk delivers value through four lenses:
- Security operations
- IT and service operations
- Observability
- Compliance evidence
Each depends on different products, skills, and budget owners, so evaluate them separately even when you buy them together.
Security Operations: SIEM, SOAR, and UEBA in Splunk
Detection speed is where security budgets win or lose. IBM's 2026 Cost of a Data Breach Report puts the global average breach at a record $4.99 million, and the average time to identify and contain a breach rose to 247 days.
ES covers detection and investigation through four main capabilities:
- Correlation searches
- Risk-based alerting, which rolls low-fidelity signals into a risk score per user or asset
- Threat intelligence management
- Case management
The Splunk Threat Research Team ships detection content through the Enterprise Security Content Update (ESCU) app. ES Premier adds SOAR playbooks, UEBA, and automated threat analysis powered by Splunk Attack Analyzer.
The caveat I give every buyer: detection quality depends on the content your team builds and maintains. Shipped detections assume CIM-mapped data, and someone has to tune them to your environment. Without that capacity in-house, a managed provider may deliver more than a SIEM nobody tunes, and our MDR comparison covers how CrowdStrike, SentinelOne, and Arctic Wolf differ.
IT and Service Operations with Splunk ITSI
ITSI moves monitoring from host health to service health. You build a service model that maps a business service to its dependencies, assign KPIs to each component, and ITSI rolls them into a single health score. When the score drops, you can see which dependency moved it.
Event analytics groups related alerts into episodes, so one failing database produces one episode instead of a flood of separate alerts. Splunk states that ITSI 5.0, released in June 2026, added Event iQ for detection and diagnosis.
ITSI is only as good as its service model. Building one takes people who understand both the application architecture and the data in Splunk. In my experience that work runs longer than the first project plan assumes.
Episodes only matter once they reach your ticketing process, so validate the ITSM integration path during the proof of concept. If you are weighing ITSI against dedicated event correlation tools, our AIOps platform comparison covers LogicMonitor, BigPanda, and Dynatrace.
Observability with Splunk Observability Cloud and AppDynamics
Observability Cloud brings APM, infrastructure monitoring, real user monitoring, synthetic tests, and logs into one SaaS product built on OpenTelemetry. That matters for lock-in, because instrumentation built on OpenTelemetry collectors and SDKs can point at a different backend later.
Splunk states that AI SRE reached general availability in late June 2026. Cisco states that Agent Observability, which evaluates and monitors AI agents including their token cost, is now available in Observability Cloud. Splunk has also announced Essentials and Premier editions for November 2026, so expect packaging to change at your next renewal.
The commercial model is separate from the platform: hosts, averaged across the month. If Datadog is the comparison, our Datadog explainer shows how its per-host billing works. The Datadog vs New Relic vs Dynatrace comparison covers the wider APM shortlist.
Compliance, Retention, and Audit Evidence in Splunk
Auditors want three things: how long you keep data, who can see it, and whether you can produce it on request. Splunk's answer starts with per-index retention.
On Cloud Platform, searchable storage (DDAS) is set in days per index. The Dynamic Data Active Archive (DDAA) holds expired data for up to 3,650 days, and restored data stays searchable for up to 30 days. Dynamic Data Self Storage (DDSS) sends expired data to a bucket you own instead.
Edge Processor and Ingest Processor can mask sensitive fields before indexing, which keeps regulated values out of the index entirely.
For public sector buyers, Splunk Cloud Platform holds FedRAMP Moderate authorization (since October 2019) and FedRAMP High (since September 2024). Splunk also lists a DoD IL5 provisional authorization in AWS GovCloud.
ES Premier reached FedRAMP Moderate on June 24, 2026, per the ES 8.5 release notes. Splunk's documentation describes Observability Cloud as still working toward FedRAMP Moderate, so confirm its status before you scope it into a federal environment.
When you compare Splunk with an XDR platform, retention is often the deciding constraint. Our XDR vs SIEM comparison covers that trade-off in detail. [Add link once the XDR vs SIEM article publishes]
See Which Splunk Products and Pricing Model Fit Your Environment
Answer the questionnaire below to see which Splunk products apply to your environment, which pricing model likely suits you, and what to compare it against.
Is Splunk Right for Your Environment?
Splunk is a strong fit for some environments and an expensive misstep in others. Your data, your team, and the licenses you already own decide which.
The Microsoft case deserves a direct sentence. If your identity, endpoint, and productivity stack is Microsoft and Sentinel is already licensed, the burden of proof sits with Splunk.
Filtering is a decision you make regardless of vendor. Splunk's own pre-index tools and pipeline products such as Cribl both do that job. Our article on the problems that surface after replacing an on-prem SIEM covers what breaks during a migration, from detection rules to retention gaps.
Splunk's capability is rarely the open question. What decides the outcome is whether your team will operate it, and whether your data volume keeps the economics sound at the second renewal as well as the first.
Evaluating Splunk against alternatives?
If you're weighing Splunk, or trying to work out whether a different SIEM or observability platform fits your data volume and team better, our platform can help. Tell us your environment and priorities, and we'll match you with the vendors worth talking to.
FAQ
What does Splunk do?
Splunk collects, indexes, and searches machine data such as logs, metrics, and events, then lets teams alert on it, build dashboards, and automate responses. Separately licensed products on the platform handle security (Enterprise Security and SOAR), IT service monitoring (ITSI), and observability (Observability Cloud and AppDynamics).
Is Splunk a SIEM?
Splunk's SIEM is one product, Splunk Enterprise Security, sold in Essentials and Premier editions, with Premier adding native SOAR and UEBA. The underlying Splunk Platform is a general machine-data platform that also runs IT operations, observability, and search workloads.
Who owns Splunk?
Cisco owns Splunk. Cisco completed the acquisition on March 18, 2024, and Splunk continues as a wholly owned Cisco subsidiary, with AppDynamics now part of the Splunk business.
What is the difference between Splunk Enterprise and Splunk Cloud Platform?
Splunk Enterprise is self-managed software you run on your own infrastructure, licensed by daily ingest or by vCPU. Splunk Cloud Platform is the Splunk-managed SaaS version on AWS, Google Cloud, or Azure, workload-based by default, and most federated search sources are available only on Cloud Platform.
How is Splunk priced?
Splunk prices by quote on four models: workload (SVCs on Cloud Platform, vCPUs on Enterprise), ingest (GB per day), activity-based (ingest plus search, Cloud Platform only), and entity (hosts, for Observability Cloud and AppDynamics). Cloud Platform service terms make workload the default, and Splunk's only published list price is Observability Cloud from $15 per host per month.
What is SPL in Splunk?
SPL, the Search Processing Language, is Splunk's pipe-based query language for searching, transforming, and visualizing indexed data. Most field extraction happens when an SPL search runs, and SPL2, a newer version, powers Edge Processor and Ingest Processor pipelines.
Is Splunk free?
Splunk offers free options with tight limits. Splunk Free indexes up to 500 MB per day on a single instance, without alerting, scheduled searches, or user authentication, and a full-featured Splunk Enterprise trial runs for 60 days. Splunk SOAR has a free Community license with 100 actions per day, and Observability Cloud has a Free Edition for 15 hosts.