Okta vs SailPoint vs Omada: identity governance compared
Okta now ships identity governance, so the real question is reach. A vendor-neutral comparison of what Okta, SailPoint and Omada can govern across SaaS, SAP, mainframe, Unix and cloud, plus SoD, deployment and licensing.
Search Okta vs SailPoint and the results repeat one line: Okta handles access, SailPoint handles governance. Okta's own documentation has moved past that answer.
Okta Identity Governance bundles Lifecycle Management, Workflows and Access Governance, and it ships access certifications, access requests, entitlement management and separation-of-duties rules.
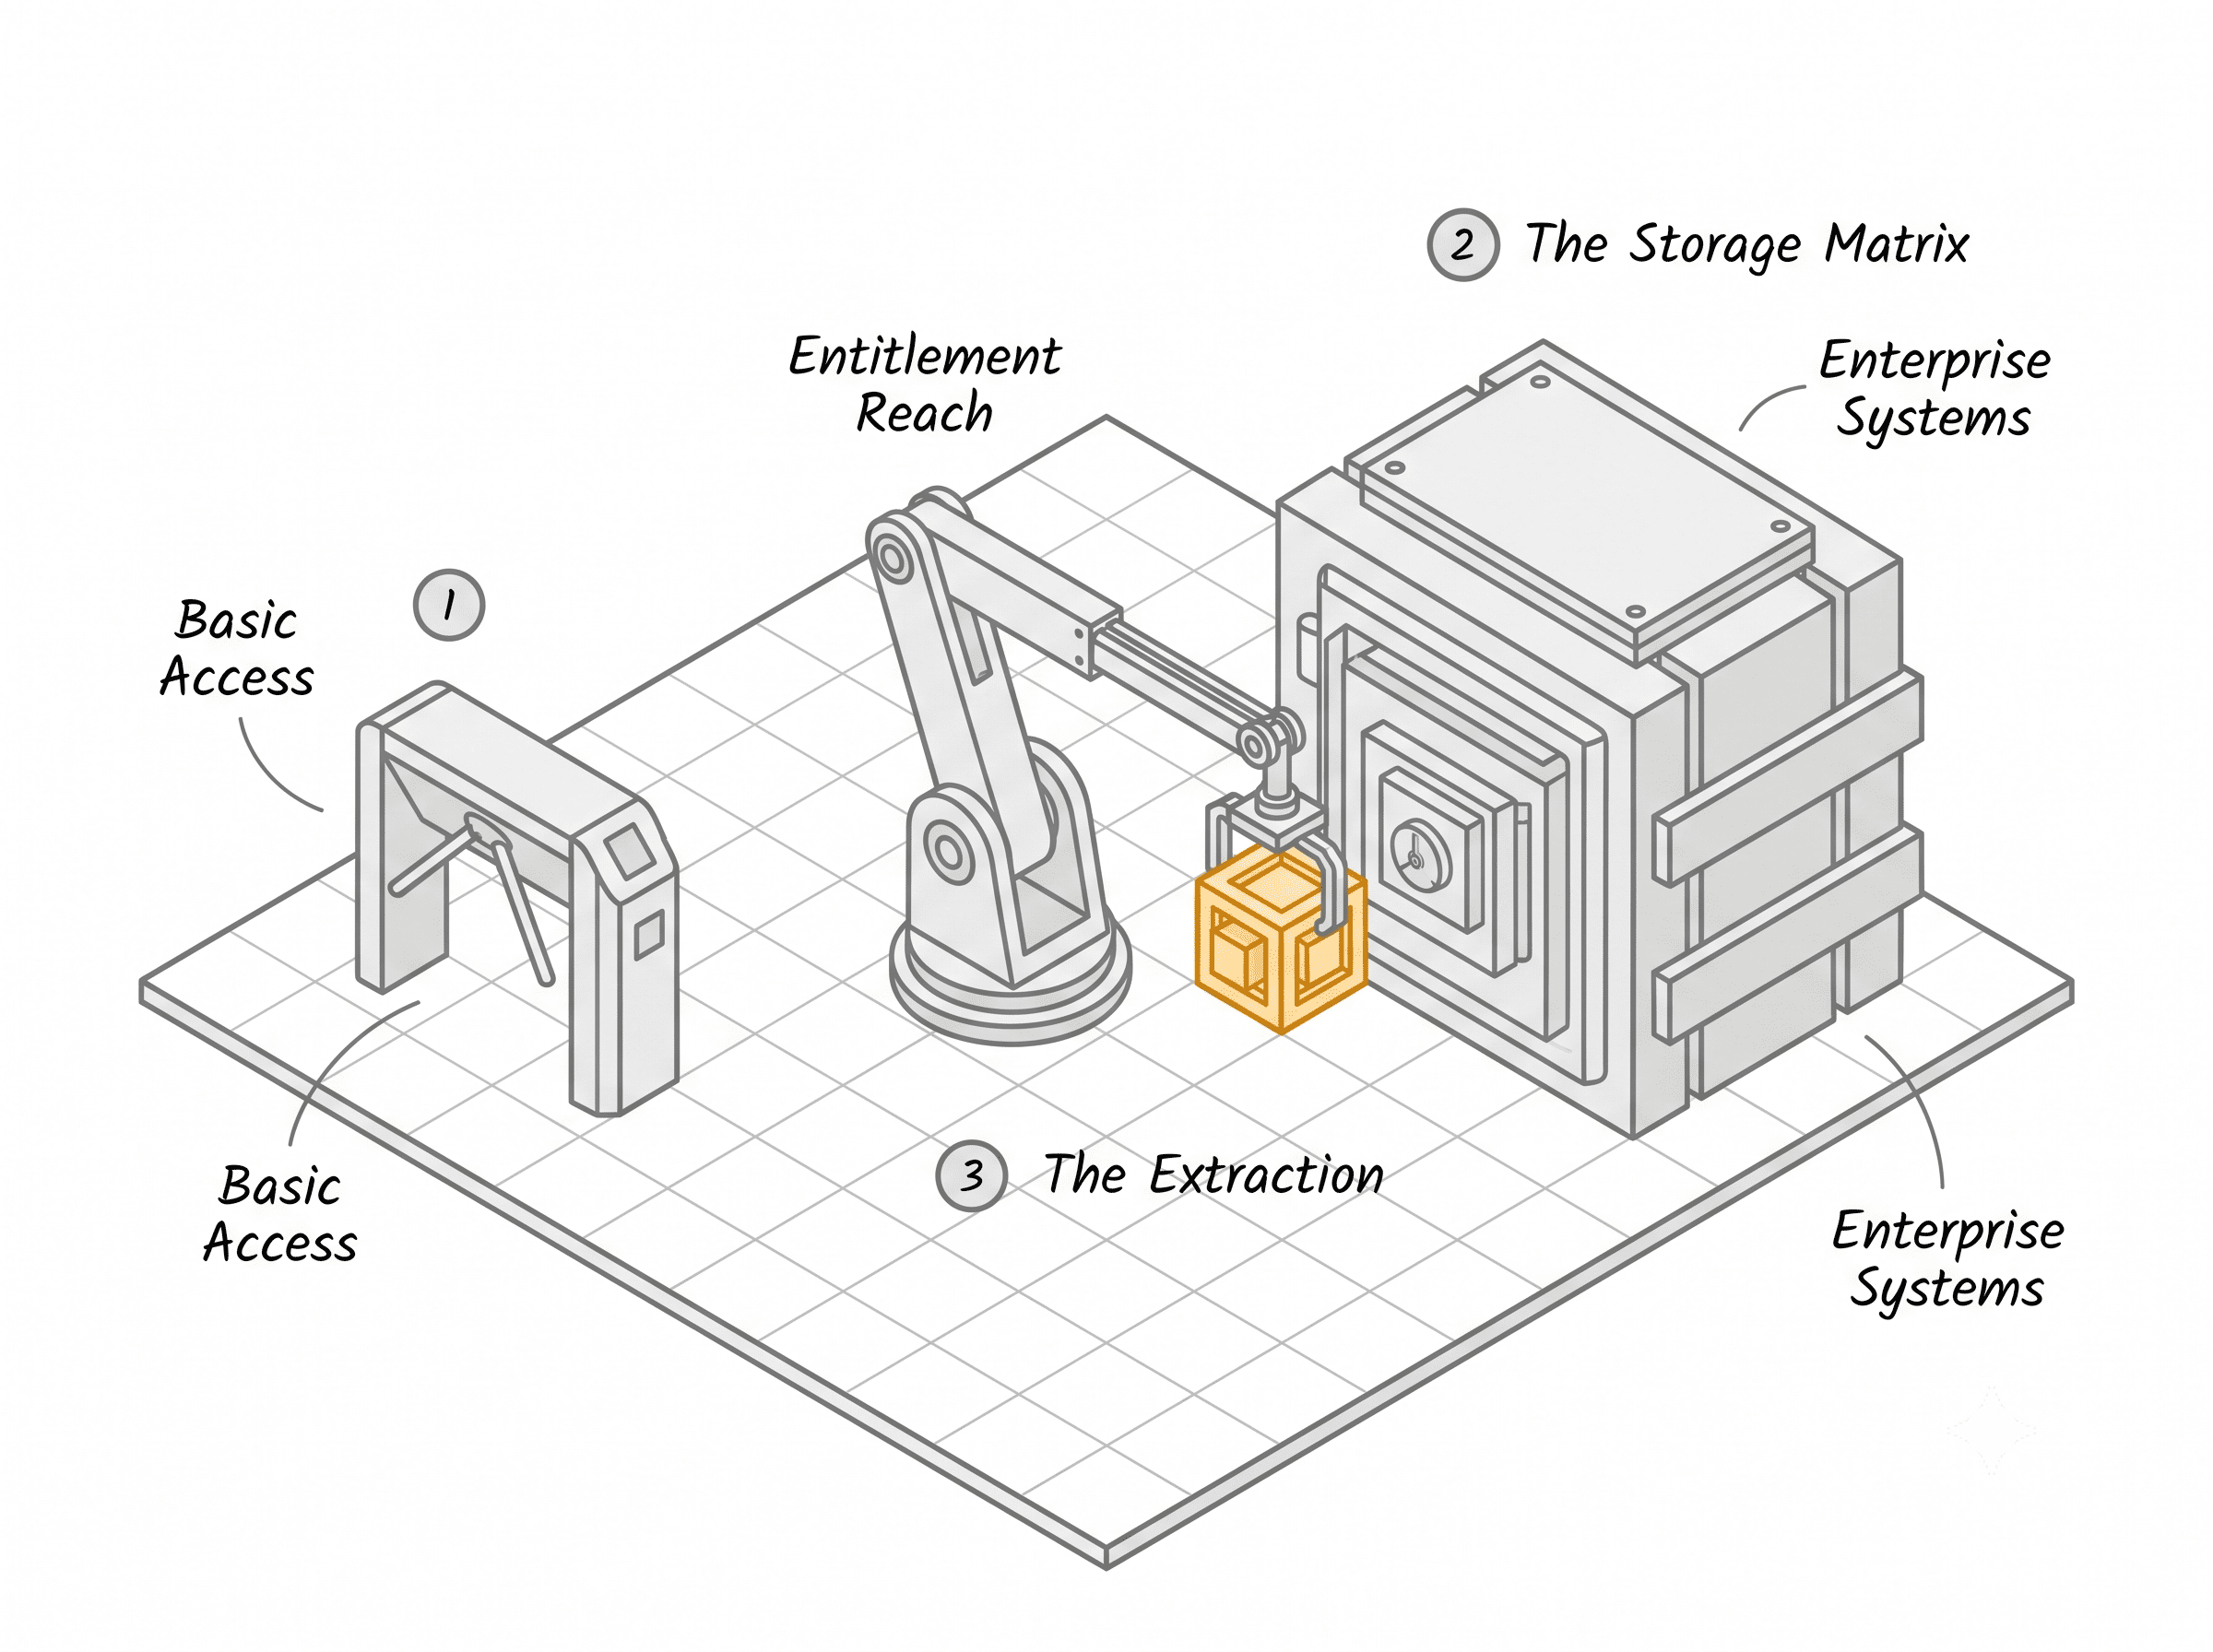
The question that decides this purchase is reach. Okta governs well inside the systems it holds entitlement data for, while SailPoint and Omada reach further into ERP, mainframe, Unix and cloud infrastructure. Each also puts part of that reach behind a module, a suite tier or a deployment choice.
If you came here for sign-in and SSO, the Ping Identity vs Okta vs OneLogin comparison covers authentication. Governance asks something else: who should have access, who approved it, and whether you can prove it on a given date.
IT Leaders Report 2026
What are your IT peers investing in 2026?
We spoke to about 1,300 IT leaders from various organisations to understand what they're evaluating. Most of it is the kind of thing you'd only hear from a peer you know well enough to ask, so we've put it in one place.
Read the report
IAM vs IGA: what is the difference?
IAM decides who can sign in. IGA decides what each person should be able to do once inside, and produces the evidence to prove it.
Identity and access management covers single sign-on, MFA, the directory and sign-in policy. Identity governance and administration covers the life of each permission: who asked for it, who approved it, whether it still makes sense, and when it was removed.
The two meet at provisioning. Creating a Salesforce account on someone's first day is lifecycle automation, and most IAM products handle it. Governance starts when you can show an auditor why that person held a specific Salesforce permission set on March 31, and who signed off.
I have sat through audits where a clean provisioning log answered none of the auditor's questions. Provisioning without approval history, periodic review and conflict rules is plumbing.
Does Okta do identity governance?
Yes. Okta Identity Governance (OIG) combines three Okta products: Lifecycle Management, Workflows and Access Governance. Okta includes it in its Workforce Identity Essentials suite and above, and the Starter and Core Essentials suites leave it out.
The qualifier matters more than the list. OIG governs at entitlement level only for applications where Okta holds entitlement data, and Okta publishes which ones those are. Everywhere else, it governs app assignment or group membership.
Okta also documents org-level ceilings. Check them against your own counts early, especially if you plan to load a large SAP role catalog.
How Okta, SailPoint and Omada are built
Okta is an identity provider that added governance. SailPoint and Omada are governance platforms that rely on an identity provider for sign-in, and SailPoint's own comparison FAQ describes Okta or Entra ID handling authentication in front of it.
Deployment follows the same split. Okta runs as SaaS. SailPoint sells a SaaS platform, which its developer documentation now names SailPoint Human Fabric (formerly Identity Security Cloud, and before that IdentityNow), plus IdentityIQ for customers who host it themselves.
Omada sells three options: multi-tenant SaaS, a private instance inside your own Azure tenant, and an on-premises edition.
Packaging is where buyers get surprised. Okta bundles governance into a suite tier. SailPoint sells Standard, Agentic Business and Agentic Business Plus suites, and places SAP-level SoD, cloud entitlement management and non-employee risk management in add-ons whose availability varies by suite. Omada publishes the least packaging detail of the three, so expect to learn it from the quote.
Where Saviynt and Microsoft Entra ID Governance fit. Both come up in almost every governance shortlist I see. Entra ID Governance is Microsoft's governance offering for Entra ID P1 and P2 customers, covering lifecycle workflows, access reviews and entitlement management. For Microsoft-centered estates, it raises the same extend-your-IdP question as Okta.
Saviynt is a governance-native platform in the same category as SailPoint and Omada. Neither is compared here, but the entitlement reach test in the next section works for both.
Can Okta replace SailPoint? It depends where your entitlements live
Okta can replace SailPoint when your audit-relevant entitlements live in systems Okta reads at entitlement level. For mainframe, Unix sudo rules and cloud infrastructure, Okta documents no governance connector, and SailPoint documents several.
An entitlement is a specific permission inside an application: a Salesforce permission set, an SAP role, a sudo rule on a Linux server. App access tells you a user can open Salesforce. Entitlement access tells you what that user can change once inside.
Where Okta reaches. Okta publishes an Apps with entitlement support list, which at the time of writing names 49 applications and the entitlement types Okta reads for each. For Salesforce, that means feature licenses, permission sets, profiles, public groups and roles. The same page notes over 300 integrations that support SCIM group provisioning, which govern through group membership instead.
Beyond SaaS, Okta's On-prem Connector reaches SAP NetWeaver ABAP roles, Oracle E-Business Suite, and Oracle, MySQL, PostgreSQL and SQL Server databases. Applications with no connector at all can import users and entitlements from CSV, and Okta calls these disconnected apps.
Active Directory groups work in Okta access requests, though they arrive as groups. If you are partway through migrating from on-prem Active Directory to Microsoft Entra ID, expect your governance answer to shift as the directory moves.
Where the specialists reach further. SailPoint documents connectors for RACF, ACF2 and Top Secret mainframes, reads Linux sudo rules, and manages GCP IAM roles through its Cloud Governance capability. Omada documents certified connectors for SAP S/4HANA, Workday and AWS. It reads SAP roles and AWS policies without writing back to them.
The app-access trap. A campaign that asks managers to confirm a user has Salesforce produces a completed certification and tells your auditor very little. The risk sits in the permission set, where one user might both create and approve the same record.
In Okta, reviewing Salesforce permission sets means turning on Entitlement Management for the Salesforce app. Okta recommends a new app instance for this, because enabling it on an existing instance marks current assignments as Custom.
Turning Entitlement Management off later deletes that app's entitlements, bundles and policies, so treat the decision as permanent. Hybrid estates feel this most, for reasons covered in why IAM breaks in hybrid Okta environments.
Separation of duties in Okta, SailPoint and Omada: native, add-on, or out of reach
All three enforce separation of duties natively. The differences sit in scope, timing, and what needs an add-on.
Okta. SoD rules live inside an application's governance settings, and each rule pairs two lists of entitlement values that should never combine. You choose whether a conflicting request is allowed, allowed with extra oversight, or blocked, with a cap of 100 rules per app and 500 per org.
One documented gap matters for SOX. Okta checks a new request against existing assignments, so two conflicting requests open at the same time can both pass. Okta's guidance is to review open requests and run campaigns to catch them.
SailPoint. SailPoint runs SoD in two tiers. Its native policy service accepts entitlements, roles and access profiles in the same conflict lists, up to 500 policies.
SAP conflicts at transaction and authorization-object level run in Access Risk Management, an add-on with prebuilt rulebooks covering more than 240 SoD risks and 8 sensitive access risks.
SailPoint's suites page lists it for Agentic Business and Agentic Business Plus only, and the module cannot simulate risks for entitlements spread across multiple SAP systems.
Omada. Omada models SoD as constraints on resources or identities. When a violation appears, the manager or constraint owner allows or blocks it, and an approver records a compensating control and a reason.
Of the three, that exception record sits closest to what an auditor asks for. Omada documents no prebuilt ERP rule sets.
Why most access certifications get rubber-stamped
Reviewers rubber-stamp when a campaign asks them to judge access they cannot interpret, in volumes they cannot finish. Three causes show up in nearly every program I have reviewed.
Okta lets you configure what reviewers see: user attributes, last application access, the previous review decision, how the access was assigned, and any SoD violation. Its Governance Analyzer adds approve or revoke recommendations, which Okta describes as a supplement to reviewer judgment.
Okta can also route reviews to resource owners, who understand an entitlement better than a line manager does. Watch remediation, though. Okta notes that access granted through group membership or group rules needs manual removal after a revoke decision.
SailPoint states its higher-tier suites include machine-learning recommendations for certifications, and its workflows can launch a fresh certification with the new manager when someone changes roles. Omada states it supports cross-system campaigns and ships more than 50 audit report templates.
Test the evidence before you test the interface. Ask each vendor for a sample campaign export and check it against what your auditor accepts. The Vanta vs Drata vs Secureframe vs Sprinto comparison covers how compliance platforms consume that evidence.
SaaS, self-hosted, and data residency options for identity governance
If policy requires governance software you host yourself, Okta leaves the shortlist. SailPoint and Omada each offer a path.
Okta runs as SaaS, and its documentation describes no customer-hosted option. Its On-prem Connector reaches internal systems through an agent that needs no inbound firewall exclusion.
SailPoint offers its SaaS platform or IdentityIQ, which runs in your data center or a public cloud account you control, and it publishes guidance for moving between the two. For mainframes, the SaaS platform connects through a Connector Gateway on a virtual appliance plus an agent on z/OS.
Omada offers the most deployment choice. Omada Identity Cloud Private, launched in May 2026, runs the full platform inside your own Microsoft Azure tenant and chosen region, and Omada positions it for organizations under DORA, NIS2 and FINMA. Its on-premises edition remains supported, with a migration service to the cloud.
Governing non-human identities and AI agents
Okta and Microsoft issue identities to AI agents, while SailPoint governs agent and machine identities created elsewhere. That split decides which product owns the problem in your estate.
Okta registers AI agents in Universal Directory with a human owner and scoped, short-lived tokens. Okta for AI Agents adds discovery of unsanctioned agents plus governance, and Okta sells it as a separate subscription. Certifying service accounts in Okta requires Okta Privileged Access.
SailPoint's Agentic Fabric discovers agents, credentials and MCP servers, assigns owners by rule, and can cut off an agent's access.
SailPoint states it connects to platforms including Microsoft 365 Copilot, Amazon Bedrock and Databricks. It governs identities wherever they were issued, which suits estates where agents come from many vendors.
Okta vs SailPoint
Okta and SailPoint now overlap on certifications, requests and SoD, so the comparison turns on reach and packaging. Okta governs its 49 entitlement-enabled apps, a set of on-prem connectors and CSV imports, inside documented org limits. SailPoint adds mainframes, Unix sudo rules, GCP IAM roles and a self-hosted option.
SailPoint's depth carries conditions. SAP authorization-level SoD needs Access Risk Management, and SailPoint's own Okta connector needs additional licensing. Okta's governance has fewer moving parts, because it shares a console and directory with your SSO.
SailPoint vs Omada
SailPoint and Omada are both governance-native, so the choice rests on mainframe reach, SAP rule content and where the software runs. SailPoint documents mainframe connectors and prebuilt SAP SoD rulebooks in a separate module.
Omada documents neither, and offers three deployment models, including a private instance in your own Azure tenant.
Omada's SoD records a compensating control and a reason on every approved exception. Omada also states a 12-week path to production through its Accelerator Package, scoped to one authoritative source, a birthright role model, self-service requests and one critical business system.
Okta vs Omada
Okta and Omada present the cleanest version of the extend-or-buy decision. Okta adds governance to an identity provider you may already run. Omada is a dedicated governance platform that expects an identity provider in front of it.
Okta's advantage is consolidation: one console, one directory, governance included from its Essentials suite. Omada's advantage is deployment control, plus connectors for SAP S/4HANA and AWS that Omada certifies itself.
I found no published Okta-to-Omada integration guide, so confirm how Omada reads Okta before you design a coexistence model.
Can you use Okta and SailPoint together?
Yes, and for many enterprises this split is the real answer: Okta handles sign-in, and SailPoint handles governance.
SailPoint documents an Okta connector that reads Okta accounts, groups and roles and provisions group membership. Okta's joint datasheet with SailPoint describes two ways to divide the work.
Watch for paying twice. Okta Essentials already includes Lifecycle Management and Access Governance, and Okta licenses every product in a suite for the same number of users. SailPoint, for its part, states that its Okta connector requires additional licensing.
What each costs, and what the meter counts
Okta meters governance per user inside a suite, SailPoint meters identities plus add-ons, and Omada publishes no licensing model. Okta is the only one with a public price list.
Its Essentials suite, the lowest tier with Identity Governance, lists at $17 per user per month billed annually, and Workforce Identity carries a $1,500 annual minimum.
SailPoint and Omada quote every deal. The meter matters more than the rate, so ask what counts as an identity and what grows the count.
Why identity governance projects fail
In my experience, governance projects fail on data, design and connector scope. Each vendor's documentation flags the trap if you read it closely.
- HR data you cannot trust. Every lifecycle rule inherits the quality of the HR feed. Omada reads Workday as a read-only authoritative source and states its control policies flag issues such as missing managers, which means the fix always happens in Workday.
- The mover problem. Okta documents that policy-assigned entitlements don't update when a group sourced outside Okta changes, so a transfer can leave old access in place. Event-driven reviews catch what attribute changes miss.
- Role and rule design. SailPoint notes most Access Risk Management implementations define between 50 and 500 rules, and recommends an SAP advisory partner beyond that. That design work consumes business owners' time, which the project plan rarely budgets.
- Connector scope. Omada's Ready tier means someone still builds a configuration package, and its 12-week accelerator covers one critical business system. Count the connectors your audit needs, then ask how many the timeline includes.
Entitlement reach assessment: which identity governance platform reaches your estate
Six documented gates decide which platform reaches your estate, starting with the hard gate on self-hosting.
Choosing on technical fit
Match the platform to where your audit-relevant entitlements live, then test your deployment and SoD requirements against each vendor's documented limits.
- Choose Okta Identity Governance when your in-scope applications sit on Okta's entitlement list or work through CSV import, SaaS-only hosting is acceptable, and your entitlement count fits inside 10,000 per org.
- Choose SailPoint when you need mainframe, Unix sudo or GCP IAM governance, SAP SoD with prebuilt rulebooks, or a self-hosted option through IdentityIQ.
- Choose Omada when governance must run in your own Azure tenant or on-premises, and your critical systems match its certified connectors.
- Run Okta with a specialist when Okta already handles sign-in and your audit scope extends beyond its entitlement list.
- Rule out Okta for on-prem reach on a FedRAMP tenant, since its on-premises entitlement connectors lack FedRAMP authorization.
Shortlisting identity governance platforms?
Shortlist pre-vetted identity governance and IAM vendors on TechnologyMatch, matched to where your entitlements live, the audits you answer to, and your hosting rules. You stay anonymous until you choose to talk, you pick who to talk to, and it's free for buyers.
FAQ
What is the difference between Okta and SailPoint?
Okta is an identity provider that includes governance in its Essentials suite, while SailPoint is a governance platform with no workforce SSO. Okta governs entitlements for its 49 listed apps, on-prem SAP NetWeaver ABAP, Oracle EBS and databases, and CSV imports. SailPoint documents wider reach, including RACF, ACF2 and Top Secret mainframes, plus SAP authorization-object SoD through its Access Risk Management add-on.
Can Okta replace SailPoint?
Okta can replace SailPoint when your audit-relevant entitlements sit in applications on Okta's entitlement list, its on-prem connectors or CSV-imported apps, and fit inside its 10,000-entitlement org limit. Okta documents no Okta Identity Governance connectors for mainframe, Unix sudo or cloud infrastructure entitlements, so estates with those systems need a governance specialist such as SailPoint.
Can SailPoint and Okta be used together?
Yes. SailPoint documents an Okta connector that reads Okta accounts, groups and roles and provisions group membership, and many enterprises run Okta for SSO and MFA with SailPoint for governance. Decide which product owns lifecycle events, and budget for the connector, which SailPoint states requires additional licensing.
Does Okta support separation of duties?
Yes. Okta Identity Governance includes native SoD rules that define conflicting entitlement combinations within an application, and you can allow, add oversight to, or block conflicting requests. Okta limits rules to 100 per app and 500 per org, and it checks requests against existing assignments, so two conflicting open requests can both pass.
What is Omada used for?
Omada is used for identity governance and administration: lifecycle driven from HR sources such as Workday, access requests, certifications, and SoD constraints with compensating controls. It documents certified connectors for SAP S/4HANA, Workday, AWS and Linux, and runs as multi-tenant SaaS, inside your own Azure tenant through Omada Identity Cloud Private, or on-premises.
Is SailPoint only for large enterprises?
SailPoint's documentation sets no size limit. It sells a Standard suite that it positioned at launch for organizations early in their identity security program, alongside its Agentic Business and Agentic Business Plus suites. SailPoint publishes no pricing or seat minimums, so request a quote at your identity count before ruling it in or out.
What is the difference between SailPoint IdentityIQ and Identity Security Cloud?
IdentityIQ is SailPoint's self-hosted governance product, run in your data center or a public cloud you control. Identity Security Cloud, formerly IdentityNow, is its multi-tenant SaaS platform, which SailPoint's developer documentation now calls SailPoint Human Fabric. Both support mainframe connectors, though some RACF interceptor features are unavailable in the SaaS product.